The False Comfort of the Blue Badge
In consumer security, few mechanisms breed more dangerous complacency than a decorative UI element masquerading as an enterprise trust anchor.
We have been conditioned by modern operating systems and web platforms to treat a verification badge as gospel. On dating apps, the blue camera checkmark is marketed as an infallible guarantee: “This person took a real-time selfie confirming their physical likeness. Relax. You’re in safe hands.”
If you are treating a Tinder or Bumble verification badge as proof that you are talking to an authentic, benevolent local singleton, you are fundamentally misunderstanding the threat model.
The blue checkmark does not certify that the person behind the screen is not a bot. It does not certify that they will not attempt to rob your cryptocurrency portfolio next Wednesday. In many cases, it does not even certify that the person chatting with you took the selfie in the first place.
Here is the operational breakdown of how commercial bot syndicates bypass dating app photo verification, why the verification marketplace is thriving at $8 a badge, and how to spot verified imposter accounts in the wild.
Threat Intelligence Brief
- The Industrial Darknet Supply Chain: Pre-verified dating accounts with blue checkmarks are sold in bulk on underground markets for between $5 and $20 per seat.
- The “Human Mule” Pipeline: Transnational fraud syndicates employ local gig workers in developing economies to complete live camera poses for pennies, transferring the verified session to remote scam operators.
- Virtual Camera Emulation: Automated bots inject synthetic video frames directly into Android virtual environment debug bridges, bypassing standard native liveness detection.
- The Architectural Answer: Upgrading from static one-time photo badges to dynamic, continuous liveness handshakes through Dating Risk Calculator.
1. How Dating App Verification Actually Works (The Weak Surface)
To understand how the system is compromised, look at the architecture of the native verification flow:
+-------------------------------------------------------------------+
|              STANDARD IN-APP PHOTO VERIFICATION FLOW              |
+-------------------------------------------------------------------+
| 1. User prompts verification in app.                              |
| 2. App requests 2-3 dynamic poses (e.g., turn left, blink, smile). |
| 3. Client captures video stream via mobile camera sensor.         |
| 4. Server-side Vision Model compares face embedding with photos.  |
| 5. If Cosine Similarity > Threshold --> "VERIFIED" badge granted.  |
+-------------------------------------------------------------------+
From an engineering perspective, this pipeline has three critical vulnerabilities:
- Client-Side Camera Interception: If the mobile operating system is rooted or run in a sandbox emulator, the video feed sent to the app can be spoofed using virtual camera loopbacks (e.g., modified Camera2 API HAL).
- One-Time State Persistence: Verification is performed once. Once the database flag
is_verified: trueis written to the user record, the user can often alter their bio, change location spoofing settings, and sometimes swap secondary photos without invalidating the badge. - Identity Decoupling: The checkmark verifies that someone with facial geometry matching the photos took a selfie. It does not verify who holds the keyboard, who owns the device, or what their criminal intentions are.
2. The Three Primary Bypass Vectors Used by Bot Syndicates
Commercial scam networks do not hack Tinder’s backend databases. They exploit the economic and operational loopholes of the verification ecosystem.
Vector 1: The Human Mule (Verification Sweatshops)
This is the most widespread and cost-effective method. In countries like the Philippines, Nigeria, or Cambodia, syndicates operate localized gig networks:
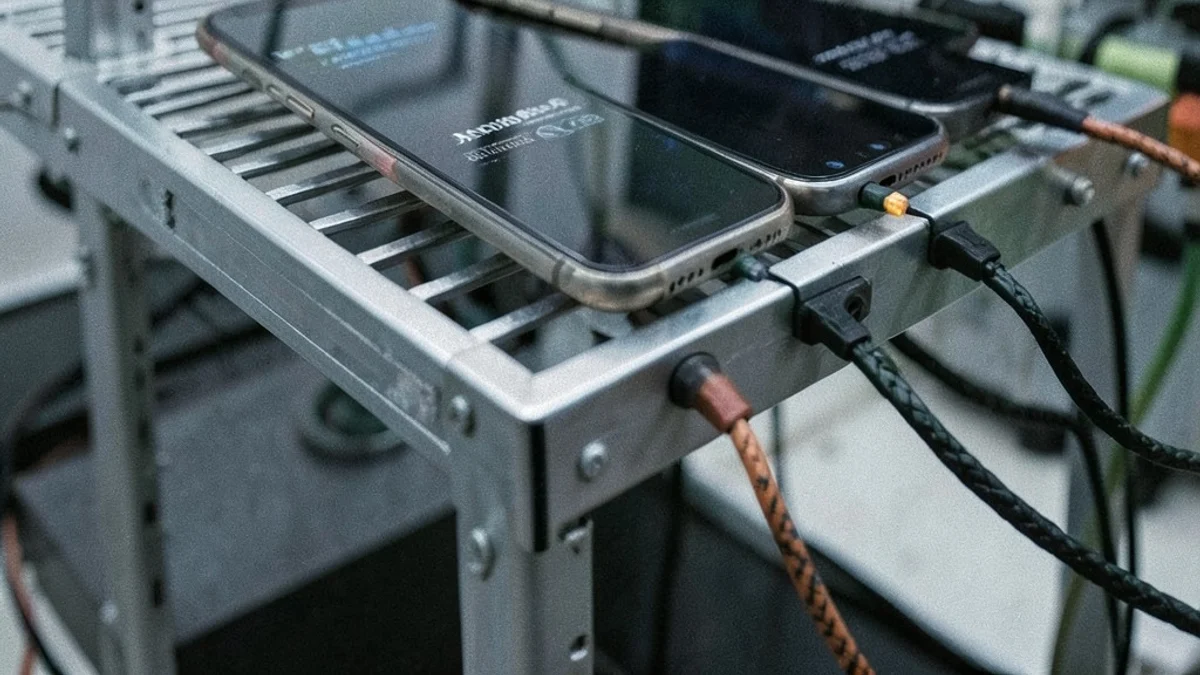
- A local individual is paid $1 to $2 to sit in front of ten mobile phones.
- They install Tinder, take their own genuine live selfies to satisfy the app’s dynamic liveness check (blinking, smiling, turning left).
- The profile is granted the blue checkmark.
- The session tokens (
auth_token,refresh_token) are immediately dumped and exported to an operator console in Manila or Phnom Penh. - The operator replaces the profile bio, updates matching preferences, and begins running high-volume romance scam scripts using a completely verified account.
Vector 2: Pre-Verified Account Marketplaces
You can purchase verified Tinder accounts with the same ease as buying a Netflix subscription. On specialized Telegram automated merchant bots and darknet forums, listings look like this:
| Tier | Account Specification | Price (USDT) | Delivery |
|---|---|---|---|
| Tier 1 | Fresh Tinder US/UK, Unverified | $1.20 | Instant (Email/Pass) |
| Tier 2 | Aged (2024), Active Karma, Unverified | $4.50 | Instant Session Cookie |
| Tier 3 | Blue Checkmark Verified (Male/Female) | $8.00 - $14.00 | Full Account Access |
| Tier 4 | Platinum Subscribed + Verified + Match Boost | $35.00 | Dedicated Proxy + Device ID |
A scammer planning a $50,000 crypto extraction considers an $8 verified account a negligible operational expense.
Vector 3: Virtual Camera Injection & Deepfake Puppetry
For higher-end operations, emulators like LDPlayer or Genymotion running custom Android ROMs are configured to pipe real-time facial puppetry software directly into the camera driver.
Software like DeepFaceLive maps the expressions of a low-wage male operator onto a high-resolution 3D mesh of a synthetic female model. When Tinder prompts: “Turn your head to the right and smile,” the operator turns his head; the synthetic model mirrors the movement with millimeter precision; the liveness model logs a successful match and issues the checkmark.
3. Warning Signs: How to Spot a “Verified” Bot in the Wild
Knowing that the badge can be bought or spoofed, you must inspect behavioral anomalies that automated or mule-operated accounts inevitably display.
                  BEHAVIORAL TRIAGE MATRIX

     [ Matches Instantly ] ──► [ Flawless Studio Photos ]
               │
               ▼
   [ Blue Checkmark Present ] ──► (False Sense of Security)
               │
               ▼
 [ Immediate Geographic Mismatch ] ──► "Traveling for business"
               │
               ▼
    [ Conversational Latency ] ──► 0.5s or robotic boilerplate
               │
               ▼
        [ SCAM PROBABILITY: HIGH (Do not trust badge) ]
Anomaly 1: The “Traveling for Business” Geolocation Trap
The account has a blue checkmark, and their location is set to your neighborhood. Yet within three messages, they claim: “I’m actually an architectural consultant currently on assignment in Zurich, but I’ll be back in London next month.” Why? The account was registered or verified locally, but the operator is managing it via an offshore server using Tinder Passport or modified GPS coordinates.
Anomaly 2: Disjointed Demographic Artifacts
Because accounts are often created by mules and later repurposed:
- The Spotify linked account will feature obscure Southeast Asian hip-hop playlists, while the bio claims they are a classical cellist from Kensington.
- The verified photo thumbnail in the app history may briefly show a completely different person before being overwritten by the scammer’s primary asset stack.
4. Moving Beyond the Static Badge: The Interactive Proof Protocol
Dating apps treat verification as a marketing feature to reduce user churn. You must treat verification as an active, continuous zero-trust security perimeter.
Never assume a profile is safe simply because an algorithm awarded it a blue SVG graphic six months ago.
When a match begins steering conversations toward finance, insists on moving to unmonitored encrypted apps, or avoids spontaneous voice/video calls, invoke the Dating Risk Calculator protocol:
“I appreciate the Tinder checkmark, but given how many hacked and purchased accounts are running around, I require an active 30-second verification on FlirtCheck before I meet anyone in person or swap numbers.”
A legitimate match will understand completely. A scam syndicate operating on purchased accounts cannot pass a secondary, independent verification challenge linked to real-time browser integrity.
Verified Profile Audit Checklist
| Checkpoint | Target Heuristic | Red Flag Result |
|---|---|---|
| Checkmark Age | When was the badge issued? | Fresh account with zero historical prompts |
| Location Coherence | Are they physically in your town right now? | Passport mode / vague excuses about foreign work |
| Photo Cohesion | Do all photos feature the same facial micro-features? | Face varies subtly across shots (different AI seeds) |
| Secondary Verification | Will they complete a quick FlirtCheck handshake? | Sudden aggression, moral outrage, or ghosting |
Frequently Asked Questions
Does Tinder know their verification system is bypassed?
Yes. It is an ongoing cat-and-mouse game. Tinder frequently updates their face-liveness models and bans emulator fingerprints. However, as long as human mules can be hired for $1 in developing nations to take live selfies, technical detection alone cannot eradicate the marketplace.
Are unverified profiles more dangerous than verified ones?
Paradoxically, unverified profiles are often less dangerous because users naturally maintain higher skepticism. The most devastating romance scams are executed from verified accounts precisely because victims let their guard down, assuming the platform has already vetted the counterparty.
Can a verified bot account steal my identity?
The bot itself won’t steal your identity inside the app, but operators use verified accounts to build rapport, extract your real phone number, Instagram handle, and work location, which are then used for targeted social engineering or identity theft.
Related Forensic Investigation
- Compare this case with our deep dive into biometric exploits: The Fake Verification Checkmark Trap: How Tinder Bot Networks Slip Past Facial Biometrics.
⚡ Quick Scan: Is Your Dating Match Real?
Instant cross-reference against verified anti-bot database and spoofing patterns.